What Is a Hybrid Deployment Model?
Learn what a hybrid deployment model is, how it balances cloud and on-premises systems, and why it matters for regulated teams.
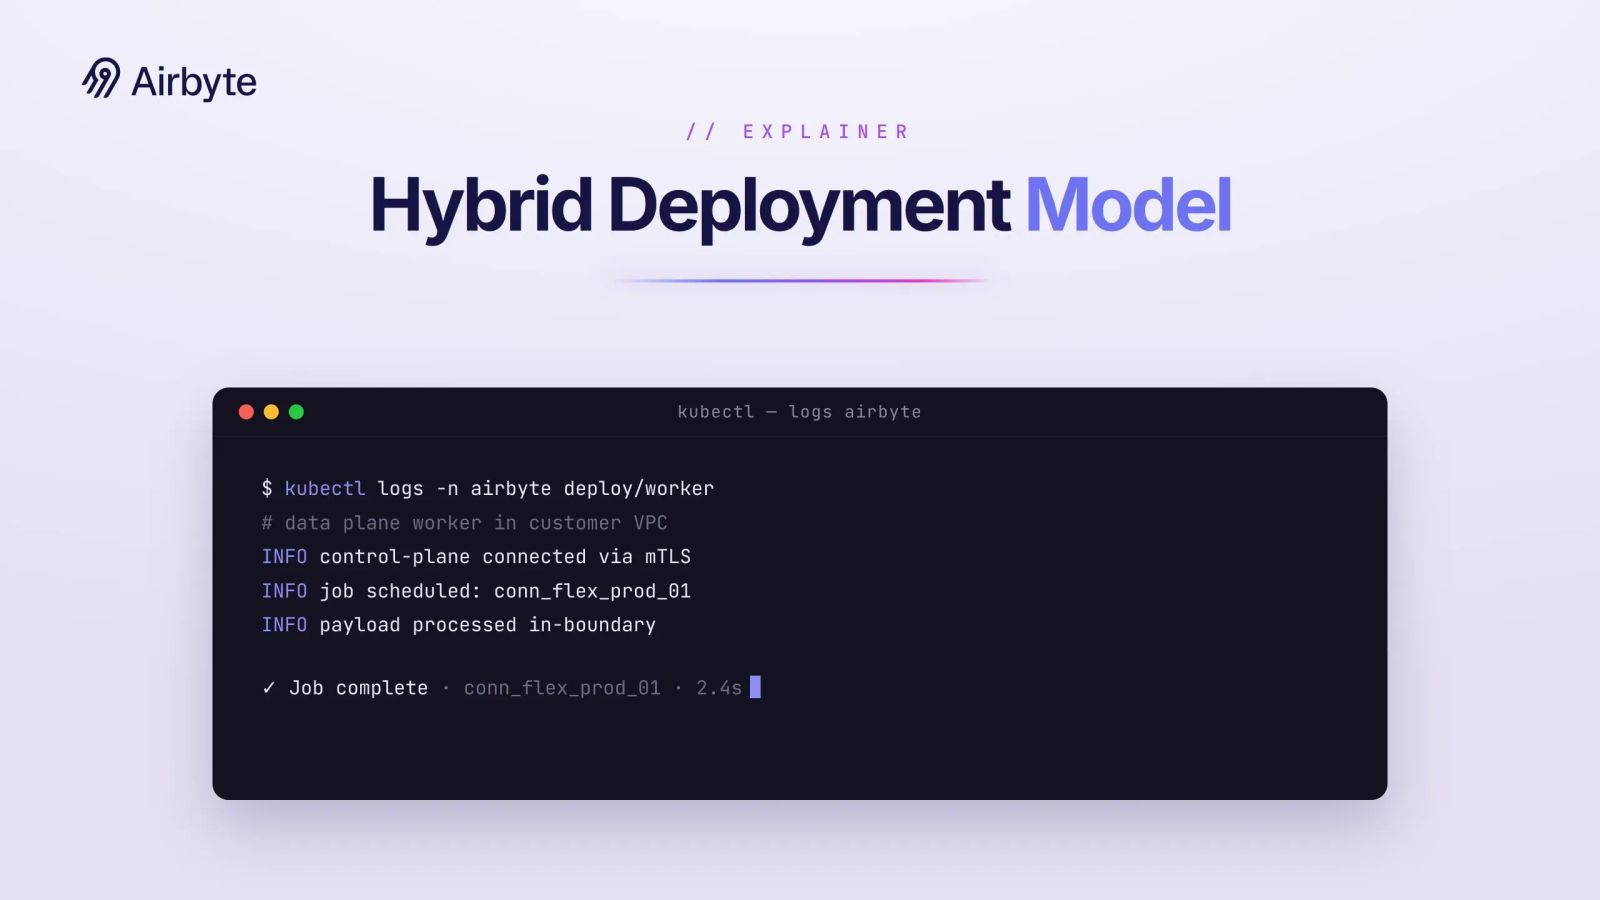
A hybrid deployment model separates a managed cloud control plane from a customer-controlled, in-boundary data plane, balancing cloud elasticity with secured local processing. Enterprises working under the General Data Protection Regulation (GDPR), Health Insurance Portability and Accountability Act (HIPAA), or the European Union (EU) Digital Operational Resilience Act (DORA) may face auditors who interpret compliance rules to mean that critical data must remain within secured networks. Metadata flows and customer-side responsibilities define the model's operating boundary and ownership requirements. Hybrid deployment shifts rather than removes operational and compliance responsibility, so your team must define who owns each control.
TL;DR
- A hybrid deployment model splits cloud-based management from in-boundary data processing, credentials, and compute.
- Local payload processing does not keep all metadata in-boundary, so document logs, schemas, metrics, lineage, and support access.
- Managed orchestration reduces some platform work, but your team still owns customer-side capacity, networking, identity, recovery, and incident response.
- Choose managed SaaS when policy permits vendor processing, hybrid when payload isolation and managed orchestration must coexist, and self-hosting for disconnected or fully sovereign operation.
What Exactly Is a Hybrid Deployment Model?
The management brain, or control plane, runs in the cloud, while the muscle, or data plane, lives inside your own network or VPC. This architecture provides managed scheduling, monitoring, and policy control and keeps payload processing in-boundary.
In this pattern, key components can include:
- Control plane in the cloud: Handles provisioning, scheduling, monitoring, and policy enforcement through public APIs for creating pipelines or updating configurations
- Data plane in your environment: Runs connectors and transformation tasks next to your databases. Credentials and records remain under your jurisdiction
Traditional hybrid cloud architectures split entire applications between public and private infrastructure. This control-plane/data-plane pattern uses cloud-based management while meeting sovereignty and compliance requirements that pure cloud deployments may not satisfy.
How Does a Hybrid Model Work in Practice?
A hybrid model works by separating cloud-based orchestration from customer-controlled execution and defining an authenticated communication boundary between them. Your outage and recovery plan must account for dependencies across both planes.
Outages and Recovery
Outage behavior is product-specific. In some architectures, customer-side runtimes remain available when they lose their control-plane connection, but they cannot apply new changes. By contrast, some managed runtimes cannot bootstrap new compute. They may eventually terminate resources after prolonged loss of control-plane communication.
Scheduled jobs may queue, become late, or run after recovery. Recovery controls should therefore include idempotent job launches, randomized exponential backoff, retry limits, and a defined policy for missed schedules.
Plane Responsibilities and Workload Movement
The control plane provides cloud-based management, orchestration, scalability, and centralized identity and policy controls, but it also introduces control-plane concentration risk. The data plane handles processing and data movement in a customer VPC or on-premises environment, where local policy enforcement and payload exposure apply, and local capacity and approved policies constrain flexibility.
The Communication Boundary
In a common design, a component in the customer-controlled data plane initiates an HTTPS connection. Mutual TLS (mTLS) protects the connection. The component then uses polling or a long-lived secure channel to communicate with the cloud control plane. The component pulls work or maintains a reverse channel over which the control plane delivers instructions. Because the customer-side component initiates the session, this pattern can avoid vendor-initiated inbound connectivity.
You can secure communication between these planes with virtual private networks (VPNs), dedicated connections, PrivateLink-style services, or egress-only internet access with strict endpoint allowlists. The data plane processes sensitive operations locally within your organization's firewall. Control-plane metadata can still flow outside the local boundary.
A boundary contract should document each flow before deployment:
Use this contract to approve boundary flows and set outage procedures before deployment.
What Are the Core Benefits of Hybrid Deployment?
Hybrid deployment can support data sovereignty, compliance controls, and managed efficiency without transferring all operations to a vendor. These benefits depend on explicit metadata boundaries and a written division of responsibility.
Data Sovereignty
Data sovereignty begins with keeping payload data and credentials in-boundary inside your VPC or on-premises infrastructure, but an auditable boundary must cover more than rows and files. An auditable inventory covers payload records, schema and table names, logs, metrics, lineage, job state, account identifiers, IP addresses, connector configuration, and support-access paths. For each category, record its destination, retention period, encryption, legal jurisdiction, and whether you can disable collection.
The public cloud may receive telemetry while customer rows remain local. Telemetry can still contain personal or confidential information. Under GDPR transfer rules, third-country remote access, including support access, may constitute a data transfer when your organization makes personal data available. Jurisdictional control covers local payload storage, bounded metadata, approved transfer mechanisms, and redaction. It also covers retention limits and audited support procedures.
Compliance Confidence
Compliance confidence depends on enforceable controls, not just deployment topology. Keeping regulated payloads local can support GDPR transfer minimization, HIPAA safeguards, and DORA resilience planning, while each framework still requires its applicable controls. Cloud-based policy engines can maintain centralized role-based access control (RBAC) and audit logs, while local systems enforce approved access, encryption, deletion, and retention policies.
DORA is in active enforcement. For financial services, DORA obligations still include information and communication technology (ICT) risk management, continuity testing, and incident reporting. They also include contractual controls, concentration-risk assessment, and exit planning. You must map the hybrid boundary to each applicable obligation.
A cloud service provider that handles ePHI is a business associate and requires an appropriate business associate agreement (BAA). You should map each technical boundary to the applicable legal and contractual control.
Managed Efficiency
Managed efficiency comes from assigning upgrades, monitoring, and orchestration to the cloud control plane while execution remains close to protected systems. The benefit depends on a written shared-responsibility model that names an owner for every operational area. Hybrid products differ materially in whether the vendor or your team patches components, upgrades Kubernetes, manages backups, or accesses diagnostic logs.
Secret rotation deserves explicit testing. Kubernetes containers using secret-backed environment variables do not receive updated values until restart. A rotation plan should include controlled restarts and a rollback plan.
Some deployments need overlapping credentials because mounted-secret configurations do not always refresh automatically. Overlapping credentials can protect long-running jobs during the change.
Confirm the responsibility split for each operational area:
Confirm these responsibilities in the contract and test them in operational runbooks.
How Does Flexibility for Growth Support Hybrid Deployment?
A hybrid deployment can grow from one on-premises database and a few cloud analytics destinations to added local or cloud capacity without requiring teams to rewrite pipeline logic. That portability is strongest for stateless workers with externalized checkpoints and compatible connector versions.
Stateful workload mobility is more limited. Moving them may require transferring checkpoints and preserving ordering guarantees. You may also need to validate network routes and IAM. Other tasks may include rotating credentials, matching runtime versions and version-skew policies, and testing state recovery and replay. Plan for downtime and data-transfer charges. Data transfer can add per-gigabyte costs even when payload data remains in the customer account. Well-tested stateless workloads may then support configuration-driven movement, while stateful workloads still require controlled cutovers.
How Does a Unified Experience Support Hybrid Deployment?
In unified platforms, a shared codebase allows both planes to operate as one system. A shared codebase can provide a single UI, identical API calls, the same connector library, and consistent observability whether jobs run in Amazon Web Services (AWS) or your data center. Teams should treat consistent runbooks and troubleshooting across execution locations as the operational test of a genuinely unified experience.
Who Benefits Most from a Hybrid Deployment Model?
Hybrid deployment benefits regulated organizations that need local payload processing with managed orchestration and can operate customer-side infrastructure. Your residency, connectivity, and operational requirements determine whether hybrid, managed SaaS, or self-hosting is the best fit.
Deployment Model Selection
Hybrid deployment suits regulated workloads that require payload isolation and managed orchestration, provided the organization has the platform expertise to operate the customer-side environment. The sovereignty spectrum runs from managed cloud to hybrid or bring your own cloud (BYOC), fully self-hosted infrastructure, and air-gapped deployment.
Compare the deployment models across these decision factors:
- Payload residency: Use managed SaaS when policy permits vendor processing, prefer hybrid or BYOC when payload processing must remain in your account or network, and prefer fully self-hosted infrastructure when every processing and management layer must remain under your control.
- Disconnected operation: Managed SaaS is usually unsuitable. Hybrid or BYOC is suitable only if the product documents offline scheduling and recovery, while fully self-hosted infrastructure is the best fit for air-gapped or indefinitely disconnected sites.
- Platform expertise: Managed SaaS is best for small teams without dedicated infrastructure staff. Hybrid or BYOC requires IAM, VPC, Kubernetes or VM, networking, and incident-response expertise, while fully self-hosted infrastructure requires the deepest platform and application ownership.
- Workload variability: Managed SaaS is a strong fit for bursty or unpredictable demand. Hybrid or BYOC is strong when local isolation and cloud-managed scaling can coexist, while fully self-hosted infrastructure is strongest for stable, predictable, high-utilization workloads that justify dedicated capacity.
- Operational ownership: In managed SaaS, the vendor owns most infrastructure operations. In hybrid or BYOC, the vendor and customer divide responsibility and document it in the contract, while in fully self-hosted infrastructure the customer owns patching, availability, backups, and recovery.
- Stateful workload portability: The vendor handles platform state in managed SaaS. Hybrid or BYOC depends on checkpoint design, runtime compatibility, and migration tooling, while fully self-hosted infrastructure gives the customer control of migration and responsibility for all work.
A retrofitted, stateful BYOC model can divide responsibility so that neither party has enough control to resolve incidents quickly. Designing architecture for hybrid operation from the start is safer than transplanting hosted software into a customer environment.
Operational Readiness
Before you select hybrid deployment, confirm that your team can manage IAM, network egress, Kubernetes or VM health, capacity, maintenance windows, checkpoints, and local incident response. You also need tested recovery procedures, clear staffing ownership, and approved support-access workflows for the customer-side environment.
Industry Fit
Hybrid deployment fits industries that combine residency or sovereignty requirements with managed orchestration needs.
Teams should choose hybrid only when residency, connectivity, and management-layer control align; otherwise, managed SaaS or fully self-hosted infrastructure may be a better fit.
How Does Airbyte Flex Help Define the Hybrid Standard?
Airbyte Flex uses a hybrid deployment model with a hybrid control plane design in which Airbyte runs the cloud control plane and the customer controls the data plane. A customer-side component initiates outbound communication, so you do not need to open an inbound port to your VPC or on-premises servers.
Key features include:
- Shared open-source codebase and connector catalog: Airbyte uses the same open-source codebase across its deployment models. The full replication catalog of 600+ connectors, along with the scheduling engine, is available across Airbyte Cloud, Self-Managed Enterprise, and Flex
- Workload portability: Your team can move compatible workloads between environments or mix them without rewriting pipeline logic
Across its platform, Airbyte supports 2M+ pipelines daily and 26B records daily, and 18% of the Fortune 500 use Airbyte.
Because the codebase is open source and deployment options share core components, this portability can reduce vendor lock-in, although state migration, networking, and operational differences can still make a move nontrivial.
Sensitive records can stay in-boundary for GDPR or HIPAA needs, while Airbyte manages Flex orchestration, monitoring, and platform upgrades. You control your data, credentials, compute boundary, IAM, networking, and capacity policies.
Why Choose Hybrid Deployment for Your Data Infrastructure?
Choose Airbyte for hybrid deployment when its division of operational responsibility matches your compliance, sovereignty, and platform requirements.
Get a demo to see how Airbyte Flex works in your boundary.
Frequently Asked Questions
What Are the Security Implications of a Hybrid Deployment Model?
Hybrid deployment can reduce payload exposure through architectural separation, but it also introduces risks around distributed IAM, metadata egress, software updates, support access and control-plane dependencies. The data plane processes sensitive information behind your firewall, while a customer-side component can connect to the control plane through an outbound-only channel, avoiding the need to expose a port for vendor-initiated inbound access. Your security team maintains direct control over local data access policies and encryption standards. Still, it must also review metadata egress, IAM scope, component credentials, software updates, remote support, and control-plane jurisdiction.
How Does Hybrid Deployment Compare to Fully Managed Cloud Platforms?
Fully managed cloud platforms place data processing and infrastructure operations with the vendor, which can create compliance challenges for regulated industries. In hybrid deployments, your team handles customer-side processing and infrastructure.
What Infrastructure Requirements Does Hybrid Deployment Need?
Hybrid deployment requires compute resources in your environment to run the data plane. Teams typically use Kubernetes clusters sized according to data volume and connector count. Network connectivity between your data plane and the cloud control plane requires stable internet or private connectivity with TLS encryption, and you can use AWS PrivateLink or VPN connections for additional security.
Can You Migrate Between Deployment Models Without Rewriting Pipelines?
Platforms that use unified codebases can let you move between deployment models or shift specific workloads without rewriting pipelines. Configuration-only migration is most realistic for stateless execution with externalized checkpoints; stateful migrations require additional cutover work.
Suggested Reads:
Integrate with 700+ apps using Airbyte
Move data from 700+ sources into warehouses, lakes, and beyond. Set up pipelines in minutes with pre-built connectors and the Connector Builder.