Benefits of a Hybrid Cloud Deployment Model
Understand the benefits of a hybrid cloud deployment model, from data residency control and elastic scale to cost and workload flexibility.
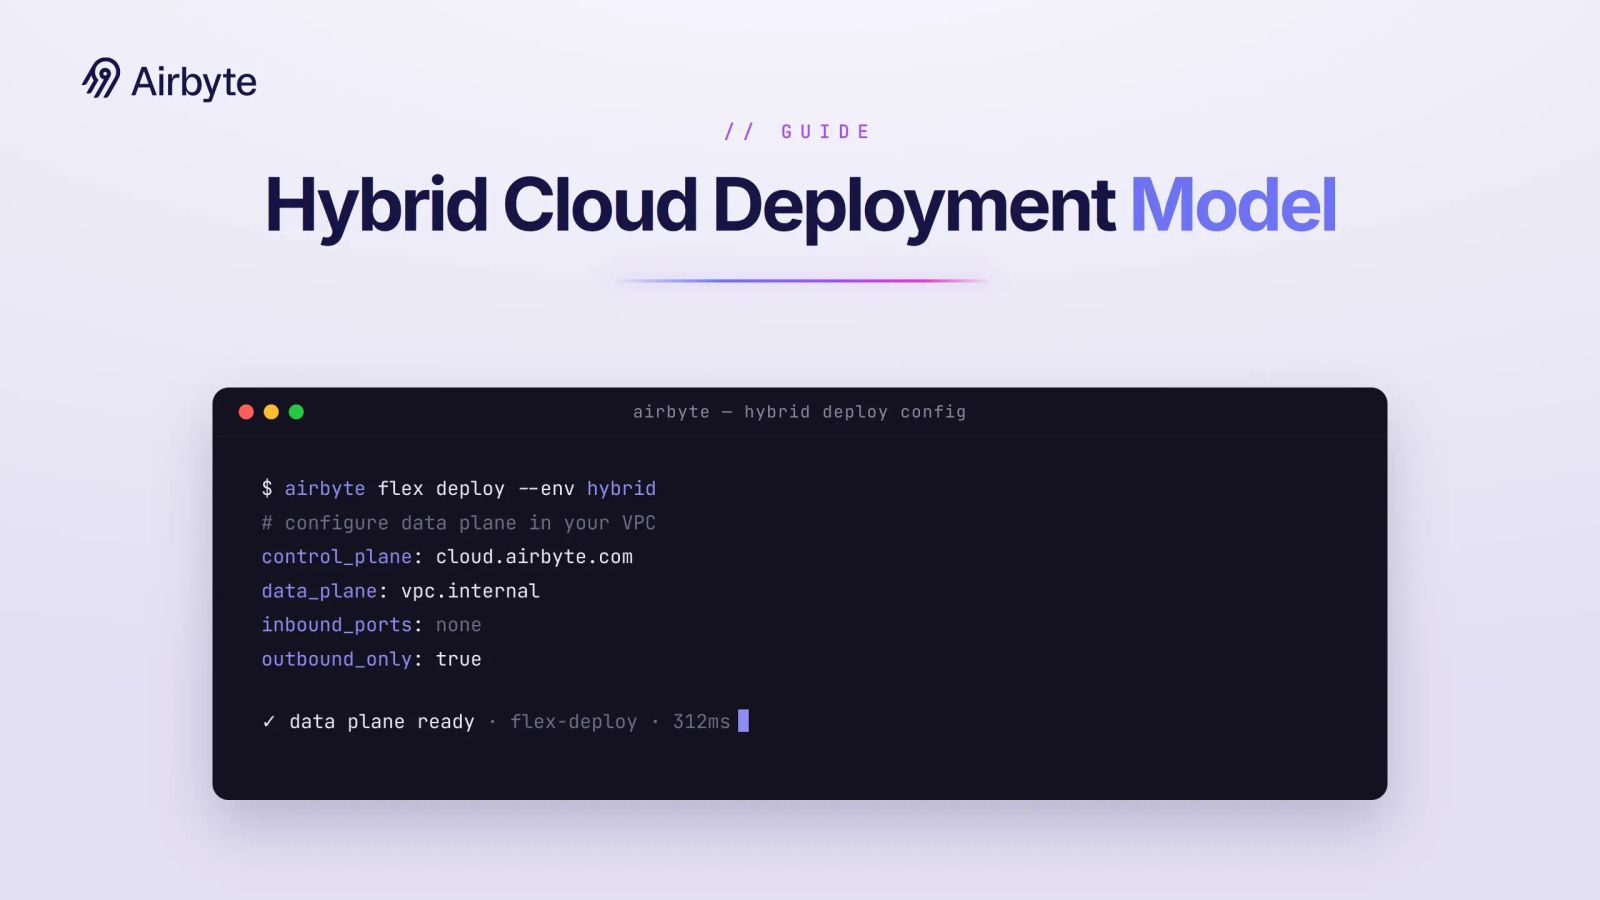
A hybrid cloud deployment model gives you workload-placement flexibility, data sovereignty, elastic capacity, cost control, and a second recovery environment, and it is worth running two infrastructure estates only when specific workloads carry constraints a single environment cannot meet. Pure cloud delivers speed and elastic scale but can reduce control over where sensitive data lives; pure on-premises preserves that control but can impose hardware purchases and months-long procurement cycles. Hybrid deployment resolves this speed-versus-sovereignty bind when legal, latency, recovery, or capacity constraints justify the added operational cost.
A hybrid architecture keeps the control plane in the cloud while running data planes on-premises, in a private cloud, or across multiple public regions, placing each workload deliberately under centralized orchestration.
TL;DR
- A hybrid cloud deployment model lets you place each workload according to sovereignty, latency, capacity, recovery, and operational requirements.
- In-boundary data planes can keep regulated data, credentials, and compute under your control while a cloud control plane manages orchestration.
- Hybrid costs become predictable only when you model utilization, staffing, interconnects, replication, egress, security, and lifecycle management.
- Adopt hybrid only when the value of precise workload placement clears the overhead of running two environments.
- The same boundary that governs replicated data also determines where AI and agent workloads can read first-party context.
What Core Benefits Can You Gain from a Hybrid Cloud Deployment Model?
You gain the most from hybrid cloud when different workloads have materially different placement constraints. Its core benefits come from matching each workload to the environment that best meets control, scale, cost, security, and recovery needs, so you get cloud elasticity without giving up control over sensitive data.
1. Greater Flexibility and Scalability
Hybrid cloud lets you treat each application the way it needs to be. Keep routine, sensitive workloads on-premises while moving bursty or experimental jobs to the cloud for extra compute power.
That portability allows seasonal peaks, such as retail holiday traffic or quarterly financial close, to expand outward. You avoid buying hardware that sits idle most of the year. Before moving a workload, assess data sensitivity, latency, utilization, transfer volume, and recovery targets. Then review software compatibility and who owns upgrades.
Applications shift most easily when you keep identity, network policy, runtime versions, and data formats consistent across environments. Without this consistency, cloud bursting can require code, dependency, or network changes.
2. Enhanced Data Sovereignty and Compliance
This model lets you keep regulated datasets, such as medical records subject to HIPAA, inside facilities you control while you orchestrate approved operations from a cloud-based control plane. You can also keep payment details subject to PCI DSS inside controlled facilities.
You can set regional data planes close to each legal jurisdiction. This arrangement supports residency requirements without duplicating full stacks everywhere. GDPR's Chapter V rules govern the conditions under which organizations may transfer personal data; the regulation has no general data-residency mandate. Sensitive tables can remain inside approved boundaries while you manage analytics, monitoring, and scheduling centrally.
Auditors can review the chain of custody, fine-grained access logs, and encryption policies for each dataset. Legal and operational sovereignty also depends on the information that crosses the boundary. Where provider access is a concern, customer-held or external key management can offer stronger separation than provider-managed encryption, although metadata and service-side resources may remain outside its protection.
3. Cost and Resource Management
Pure on-premises environments require major capital outlays, while pure cloud setups can surprise you with volume-driven bills. Hybrid approaches can align spend with behavior. You can keep steady, predictable workloads running on equipment you already own while using pay-as-you-go cloud capacity to cover unexpected spikes and avoid rushed hardware purchases.
The comparison must include more than server capital expenditure and cloud compute rates. Model utilization, facilities, power, cooling, storage, support, hardware refreshes, private interconnect port charges, cross-region traffic, operational egress, software licenses, observability, security tooling, staffing, and 24×7 support. Omitting these costs distorts total cost of ownership, and local processing reduces egress only when it also avoids recurring transfers or replication across the boundary.
Staffing demands may decrease when the provider manages orchestration. Customer-run data planes still require capacity planning, incident response, secret rotation, and coordination around supported runtime versions. A more even expense curve depends on high utilization for stable workloads and controlled burst capacity. Your platform team must also operate both environments without duplicating tools and roles.
4. Improved Security Posture
Mission-critical databases can operate without internet-facing endpoints. You can isolate them behind on-premises firewalls and permit only authenticated outbound connections to the cloud control plane. This configuration reduces direct inbound network exposure.
You own the data plane, so you decide which encryption standards, key managers, and column-level hashing rules apply to each table. Segmentation by workload lets you tighten policies around customer PII while relaxing them for non-sensitive log data. This approach aligns controls more precisely with risk than blanket policies.
Outbound-only networking still leaves credential, control-plane, software supply-chain, and exfiltration risks. A stolen control-plane token may authorize legitimate-looking jobs, and a compromised agent image may execute inside the data plane. An encrypted outbound channel can also conceal malicious traffic.
Treat the control plane as a privileged administrative system. Require phishing-resistant MFA, short-lived workload credentials, and signed and scanned agent images. Enforce least-privilege job permissions, restrict egress destinations, add approval controls for sensitive pipelines, and store audit logs within the relevant jurisdiction.
5. Business Continuity and Disaster Recovery
Redundancy across two distinct environments makes outages less threatening when you design applications and data for failover. If a local data center floods, cloud replicas can take over. If a cloud region falters, pre-provisioned on-premises systems can keep serving users. This dual stance can reduce single points of failure and shrink recovery time objectives.
You must define replication lag, recovery point objectives, recovery time objectives, failover authority, DNS or routing changes, secret availability, and how much capacity you reserve at the recovery site. Recovery procedures should minimize dependence on control-plane operations because an incident may make scheduling and administrative APIs unavailable. For banking entities, this planning can support DORA requirements for ICT risk management, which regulators actively enforce.
Use these checks to define disconnected behavior before an incident:
You can automate failover routing and maintain off-site backups without financing a second full physical site. Still, higher uptime follows only when you capacity-test and regularly exercise the recovery path. Those same placement choices determine which records cross boundaries and which team owns job execution, which is where integration and analytics come in.
How Can the Hybrid Model Improve Your Data Integration and Analytics?
Hybrid deployment improves data integration by separating centralized orchestration from the infrastructure that processes and loads records. Cloud orchestration schedules and monitors jobs while local data planes handle extraction, transformation, and loading, so sensitive processing stays inside your network.
Approved operational metadata crosses the network boundary while record payloads can remain local. Classify schema names, table names, row counts, error messages, query text, and logs before you allow them across, because operational metadata can reveal sensitive business context even when payloads never leave.
Local compute reduces query latency and avoids some recurring transfer charges, which matters when regional teams need dashboards that refresh in seconds. The same deployment can stream high-volume CDC to Kafka and run nightly batch loads to Snowflake under one set of policies, giving you regional data placement, shared governance, and a mix of continuous and batch analytics. Validate wide-area latency, throughput limits, retry behavior, checkpoint storage, clock synchronization, and duplicate handling before placing a single pipeline across distant environments.
How Can Hybrid Cloud Support Your Innovation and AI Readiness?
Hybrid deployment lets teams treat AI capacity as a workload-placement decision. When data-placement and transfer policies permit, teams can run eligible AI workloads on elastic cloud compute while keeping approved source-data preparation in-boundary, so experimentation scales without moving regulated data out of controlled environments.
What Challenges Can the Hybrid Model Solve for You That Others Don't?
Hybrid cloud addresses the conflict between public cloud scaling and local control by placing workloads based on cost, capacity, compliance, latency, and operational requirements, and it calls for shared governance to manage operational complexity across two environments. The model exchanges single-environment simplicity for selective placement, and it pays off when the value of precise placement clears the overhead of two estates.
A single workload can score differently across placement criteria, so the strongest legal, latency, recovery, or operational constraint should drive the decision. One API, unified governance, and shared observability reduce duplicate tooling; fragmented identity, policy, inventory, and lifecycle management increase tool sprawl, monitoring blind spots, and staffing needs.
Choose hybrid when you manage mixed legacy and greenfield portfolios, have hard latency constraints, face significant data gravity, or require strict operational control. Cloud-first is simpler for greenfield environments without residency or latency constraints, sovereign SaaS can meet location and operational requirements without a customer-run data plane, and fully on-premises deployment fits steady workloads that need disconnected operation and dedicated infrastructure expertise.
Use these criteria to place each workload on the sovereignty spectrum:
After placement, assign patching and incident ownership, then test recovery and exit paths so the operating model can sustain the decision.
How Does Airbyte Flex Deliver These Hybrid Cloud Benefits?
Airbyte Flex is Airbyte's hybrid deployment offering, and it maps onto the control-plane and data-plane split described above. Airbyte operates the control plane while the data plane, along with your records, credentials, keys, and compute, runs in your environment, though some metadata such as cursor and primary-key values sits in the control plane. Across Airbyte deployments, customers move 26 billion records daily, and 18% of the Fortune 500 use Airbyte.
Architecture That Maintains Security Boundaries
The architecture uses the following boundary controls:
- Cloud-hosted control plane schedules jobs, monitors performance, and manages Flex platform upgrades
- One Airbyte instance can cover multiple regions through multiple workspaces, with each regional workspace using the appropriate customer-controlled data plane in your own VPC or data center
- The data plane initiates all communication outbound
- The architecture opens no inbound ports
Together, these controls reduce direct inbound network exposure and restrict communication to outbound connections that the data plane initiates. Consistent software across deployment types keeps that separation operable as workloads move between environments.
Unified Codebase Across All Deployments
Airbyte Flex keeps connectors, processing steps, and APIs consistent across deployment models, with deployment-specific validation.
- Full library of 700+ connectors, aligned with Airbyte Cloud
- Same processing steps and API across deployments, though API base URLs vary by deployment type
- You can reuse pipeline definitions across regions and deployment types, subject to credential, endpoint, networking, and policy changes
This consistency can reduce duplicate pipeline development and vendor lock-in while preserving deployment-specific controls. Airbyte's open-source foundation, shared connectors, API, and reusable pipeline definitions support portability, but credentials, endpoints, networking, and policies still require deployment-specific work.
Enterprise Security Features
Airbyte Flex provides controls for credentials, sensitive data, and auditing across hybrid deployments.
- Customer-controlled credentials
- PII masking and data protection
- Organization-level audit logging on supported paid tiers, for events such as connection, permission, and source changes
Before production rollout, document the outbound endpoints and certificates that the data plane requires. Define the metadata you permit to cross the boundary, credential-expiry behavior, and log retention during disconnection. Also document supported runtime versions, upgrade ownership, and the recovery sequence after connectivity returns. The same replicated records are what an in-boundary retrieval stack indexes, so agent reads inherit the boundary and access controls the pipeline already enforces.
Where Should You Start With Hybrid Cloud Deployment?
Hybrid deployment earns its added operational cost only where specific workloads carry legal, latency, recovery, or capacity constraints that a single environment cannot meet. Score each candidate workload against those constraints, then test the operating, recovery, and exit plans before you commit to a landing zone.
Airbyte covers the range from a fully managed cloud service to Flex, which keeps execution, credentials, and compute inside your environment while Airbyte runs orchestration across cloud, hybrid, and on-premises deployments.
Get a demo to walk through how Airbyte Flex would fit your hybrid deployment and data sovereignty requirements.
Frequently Asked Questions
What Is the Difference Between Hybrid Cloud and Multi-Cloud?
Hybrid cloud connects on-premises infrastructure with cloud environments under unified management, while multi-cloud uses multiple cloud providers, such as AWS and Azure, and can consist entirely of public cloud platforms. Hybrid focuses on deployment flexibility and data sovereignty, while multi-cloud focuses on distributing services across public cloud platforms. Either model can increase operational complexity if you leave identity, policy, observability, and lifecycle management fragmented.
How Does a Hybrid Cloud Deployment Model Affect Your Data Latency?
Hybrid deployments can reduce latency by processing data near its source. Workflows that synchronously cross the boundary inherit wide-area latency, jitter, and availability constraints. Measure the complete path and keep latency-sensitive transaction loops within one environment where possible.
Can You Reduce Overall Infrastructure Costs With Hybrid Cloud?
Yes, when savings from highly utilized owned infrastructure and temporary cloud capacity exceed connectivity, data movement, tooling, staffing, and lifecycle costs. Set workload placement thresholds, model egress, and capacity-test burst and recovery paths to keep costs predictable.
Which Compliance Frameworks Can You Support With Hybrid Deployment?
Hybrid architectures can support frameworks requiring strong location, transfer, security, or operational controls, including GDPR for EU personal-data transfers, HIPAA for healthcare records, PCI DSS for payment card data, DORA for financial-sector operational resilience, and export controls like ITAR. GDPR regulates transfer conditions and has no general residency mandate, while ITAR's encryption carve-out applies only under specific conditions for unclassified technical data. Regulators generally focus on risk assessment, institutional controls, tested resilience, and documented exit planning.
Integrate with 700+ apps using Airbyte
Move data from 700+ sources into warehouses, lakes, and beyond. Set up pipelines in minutes with pre-built connectors and the Connector Builder.